Quick Start - VPC
Prerequisites
- Exoscale CLI download the latest binary for macOS, Linux or Windows from GitHub
- Exoscale Account sign in or register.
- API Key/Secret
configured via the CLI with
exo config. - SSH Key registered in your Exoscale account, to connect to the instances.
First Steps via CLI
Create a VPC
Create a VPC named my-first-vpc:
$ exo networking vpc create my-first-vpc
 ✔ Creating VPC "my-first-vpc"... 0s
┼─────────────┼──────────────────────────────────────┼
│     VPC     │                                      │
┼─────────────┼──────────────────────────────────────┼
│ ID          │ cdaa9663-634d-4abd-94a3-fc2b32c4854a │
│ Name        │ my-first-vpc                         │
│ Description │                                      │
│ Default     │ false                                │
│ Zone        │ ch-gva-2                             │
│ Created At  │ 2026-09-09 07:31:15 +0000 UTC        │
│ Labels      │ n/a                                  │
│ Subnets     │ -                                    │
┼─────────────┼──────────────────────────────────────┼
Create a Subnet
Add a Subnet to the VPC with the chosen private IPv4 range:
$ exo networking vpc subnet create my-first-vpc my-first-subnet --address-family inet4 --address-space private --ipv4-block 10.42.0.0/16
 ✔ Creating Subnet "my-first-subnet"... 0s
┼────────────────┼──────────────────────────────────────┼
│   VPC SUBNET   │                                      │
┼────────────────┼──────────────────────────────────────┼
│ ID             │ d557ef4e-c481-4ba4-872e-4c6b53705be8 │
│ Name           │ my-first-subnet                      │
│ Description    │                                      │
│ Zone           │ ch-gva-2                             │
│ Created At     │ 2026-09-09 07:32:39 +0000 UTC        │
│ Address Family │ inet4                                │
│ Address Space  │ private                              │
│ IPv4 Block     │ 10.42.0.0/16                         │
│ Labels         │ n/a                                  │
│ Instances      │ -                                    │
┼────────────────┼──────────────────────────────────────┼
Create and Attach Instances
Create the first instance:
$ exo compute instance create instance-A --template "Linux Ubuntu 26.04 LTS 64-bit" --ssh-key my-ssh-key
 ✔ Creating instance "instance-A"... 21s
┼─────────────────────────────────────────┼──────────────────────────────────────┼
│            COMPUTE INSTANCE             │                                      │
┼─────────────────────────────────────────┼──────────────────────────────────────┼
│ ID                                      │ 324d7bb3-0a1c-4bd8-abc5-9a1cd8109196 │
│ Name                                    │ instance-A                           │
│ Creation Date                           │ 2026-09-09 07:34:26 +0000 UTC        │
│ Instance Type                           │ standard.medium                      │
│ Template                                │ Linux Ubuntu 26.04 LTS 64-bit        │
│ Zone                                    │ ch-gva-2                             │
│ Anti-Affinity Groups                    │ n/a                                  │
│ Deploy Target                           │ -                                    │
│ Security Groups                         │ default                              │
│ Private Instance                        │ No                                   │
│ Elastic IPs                             │ n/a                                  │
│ Public IP                               │ inet4                                │
│ IP Address                              │ 85.217.161.236                       │
│ IPv6 Address                            │ -                                    │
│ Vpc                                     │                                      │
│ Vpc Subnets                             │ n/a                                  │
│ Private Networks                        │ n/a                                  │
│ SSH Keys                                │ n/a                                  │
│ Disk Size                               │ 50 GiB                               │
│ State                                   │ running                              │
│ Labels                                  │ n/a                                  │
│ Secure Boot                             │ false                                │
│ Tpm                                     │ false                                │
│ Reverse DNS                             │                                      │
│ Application-Consistent Snapshot enabled │ false                                │
┼─────────────────────────────────────────┼──────────────────────────────────────┼
Attach it to the Subnet:
$ exo compute instance attach-to-subnet instance-A my-first-vpc my-first-subnet
 ✔ Attaching instance "instance-A" to Subnet "my-first-subnet"... 3s
┼─────────────────────────────────────────┼──────────────────────────────────────┼
│            COMPUTE INSTANCE             │                                      │
┼─────────────────────────────────────────┼──────────────────────────────────────┼
│ ID                                      │ 324d7bb3-0a1c-4bd8-abc5-9a1cd8109196 │
│ Name                                    │ instance-A                           │
│ Creation Date                           │ 2026-09-09 07:34:26 +0000 UTC        │
│ Instance Type                           │ standard.medium                      │
│ Template                                │ Linux Ubuntu 26.04 LTS 64-bit        │
│ Zone                                    │ ch-gva-2                             │
│ Anti-Affinity Groups                    │ n/a                                  │
│ Deploy Target                           │ -                                    │
│ Security Groups                         │ default                              │
│ Private Instance                        │ No                                   │
│ Elastic IPs                             │ n/a                                  │
│ Public IP                               │ inet4                                │
│ IP Address                              │ 85.217.161.236                       │
│ IPv6 Address                            │ -                                    │
│ Vpc                                     │ my-first-vpc                         │
│ Vpc Subnets                             │ my-first-subnet 10.42.145.150        │
│ Private Networks                        │ n/a                                  │
│ SSH Keys                                │ n/a                                  │
│ Disk Size                               │ 50 GiB                               │
│ State                                   │ running                              │
│ Labels                                  │ n/a                                  │
│ Secure Boot                             │ false                                │
│ Tpm                                     │ false                                │
│ Reverse DNS                             │                                      │
│ Application-Consistent Snapshot enabled │ false                                │
┼─────────────────────────────────────────┼──────────────────────────────────────┼
Create and attach a second instance:
$ exo compute instance create instance-B --template "Linux Ubuntu 26.04 LTS 64-bit" --ssh-key my-ssh-key
$ exo compute instance attach-to-subnet instance-B my-first-vpc my-first-subnet
Allow Traffic Between the Instances
Create a Security Group that allows the instances to ping each other and accepts SSH connections from any address:
$ exo compute security-group create my-sg
[...]
$ exo compute security-group rule add my-sg --protocol tcp --flow ingress --port 22 --network 0.0.0.0/0
[...]
$ exo compute security-group rule add my-sg --protocol icmp --flow ingress --icmp-type 8 --security-group my-sg
 ✔ Adding rule to Security Group "my-sg"... 24s
┼──────────────────┼────────────────────────────────────────────────────────────────────────────────────────────┼
│  SECURITY GROUP  │                                                                                            │
┼──────────────────┼────────────────────────────────────────────────────────────────────────────────────────────┼
│ ID               │ 699977e4-0403-478c-9b61-7dd347643e98                                                       │
│ Name             │ my-sg                                                                              │
│ Description      │                                                                                            │
│ Ingress Rules    │                                                                                            │
│                  │   dc712e4c-9998-4823-a49e-edc2413a8b53      ICMP   SG:my-sg   ICMP code:0 type:8   │
│                  │   718f4c0b-711f-4adb-a84b-29b67b458de3      TCP    0.0.0.0/0          22                   │
│                  │                                                                                            │
│ Egress Rules     │ -                                                                                          │
│ External Sources │ -                                                                                          │
│ Instances        │ -                                                                                          │
┼──────────────────┼────────────────────────────────────────────────────────────────────────────────────────────┼
Add both instances to the Security Group:
$ exo compute instance security-group add instance-A my-sg
$ exo compute instance security-group add instance-B my-sg
Confirm Private Connectivity
Connect to instance-A over SSH and ping the VPC address of instance-B:
ubuntu@instance-A:~$ ping 10.42.13.243
PING 10.42.13.243 (10.42.13.243) 56(84) bytes of data.
64 bytes from 10.42.13.243: icmp_seq=1 ttl=64 time=0.442 ms
64 bytes from 10.42.13.243: icmp_seq=2 ttl=64 time=0.340 ms
64 bytes from 10.42.13.243: icmp_seq=3 ttl=64 time=0.511 ms
^C
--- 10.42.13.243 ping statistics ---
3 packets transmitted, 3 received, 0% packet loss, time 2032ms
rtt min/avg/max/mdev = 0.340/0.431/0.511/0.070 ms
The Security Group blocks traffic on other protocols or ports until you add a rule to allow it.
First Steps via Portal
This quick start guide will demonstrate how to create a first VPC and one Subnet via the Portal.
Create a VPC
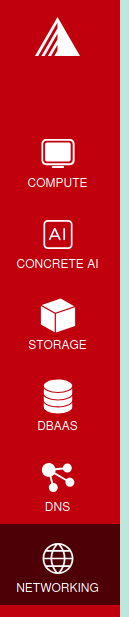
Navigate to the Networking view and the VPC tab:
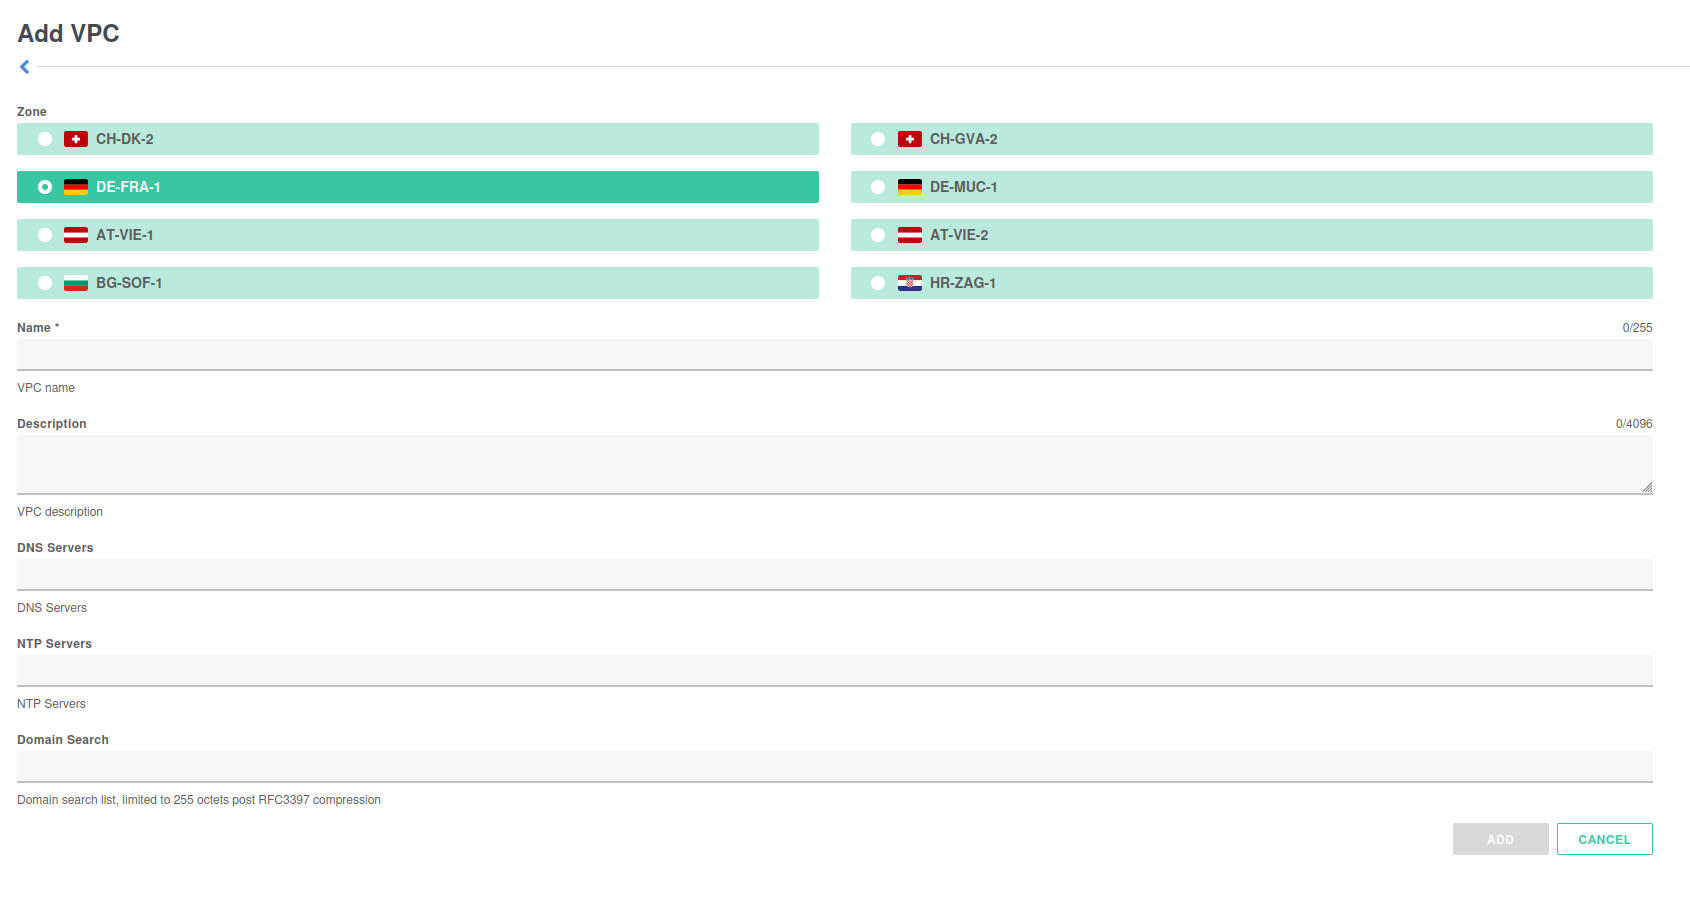
Click the Add button on the top, then enter the location of the VPC, its name and the other optional fields if required
Note
Even if you haven’t created any VPC, you’ll see that you already have one default VPC in each zone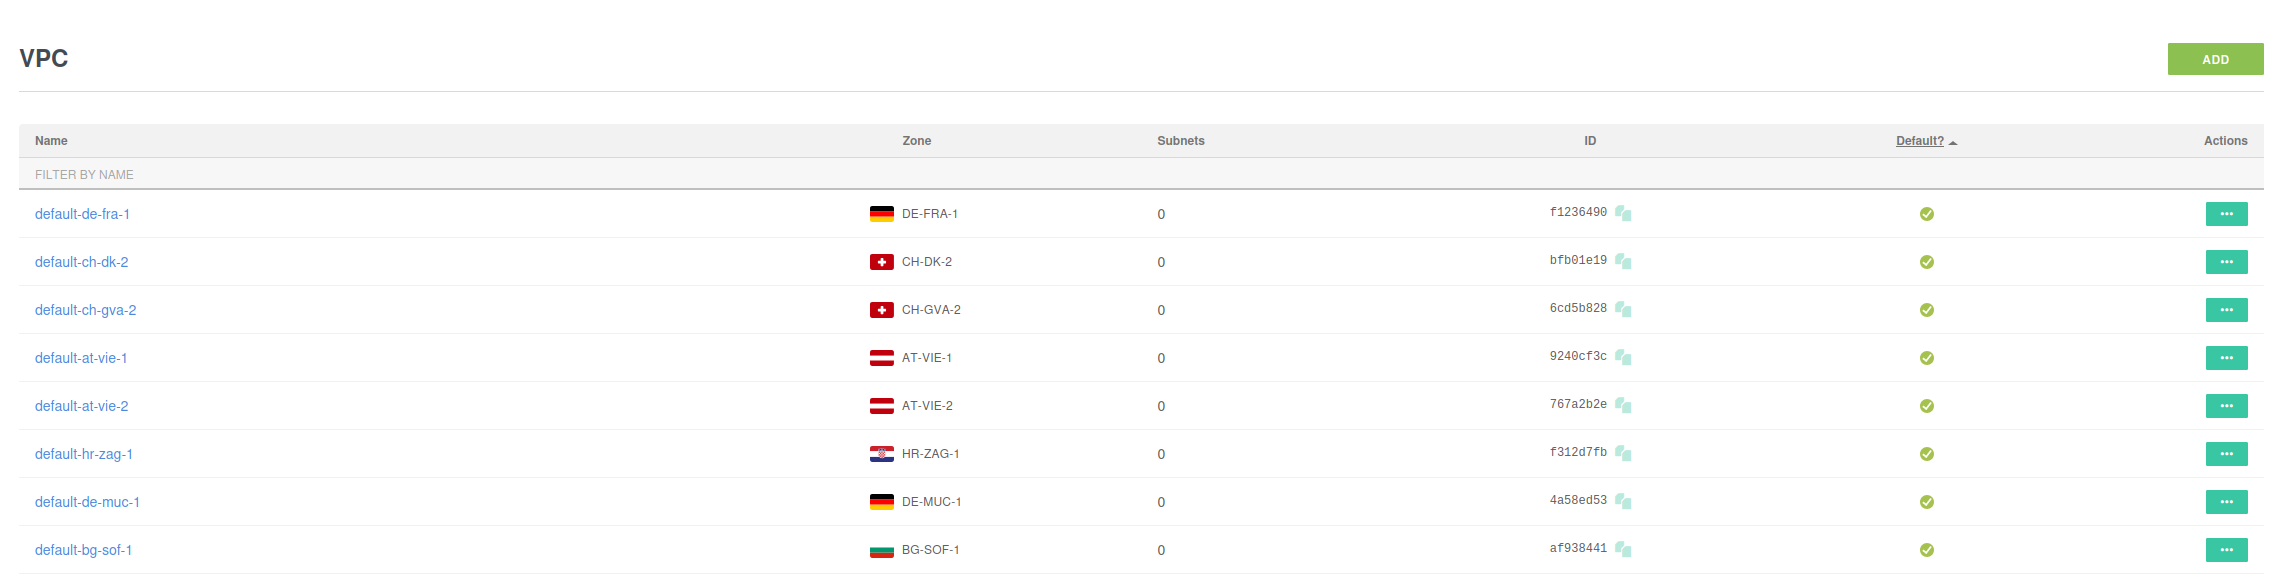
Create a VPC Subnet
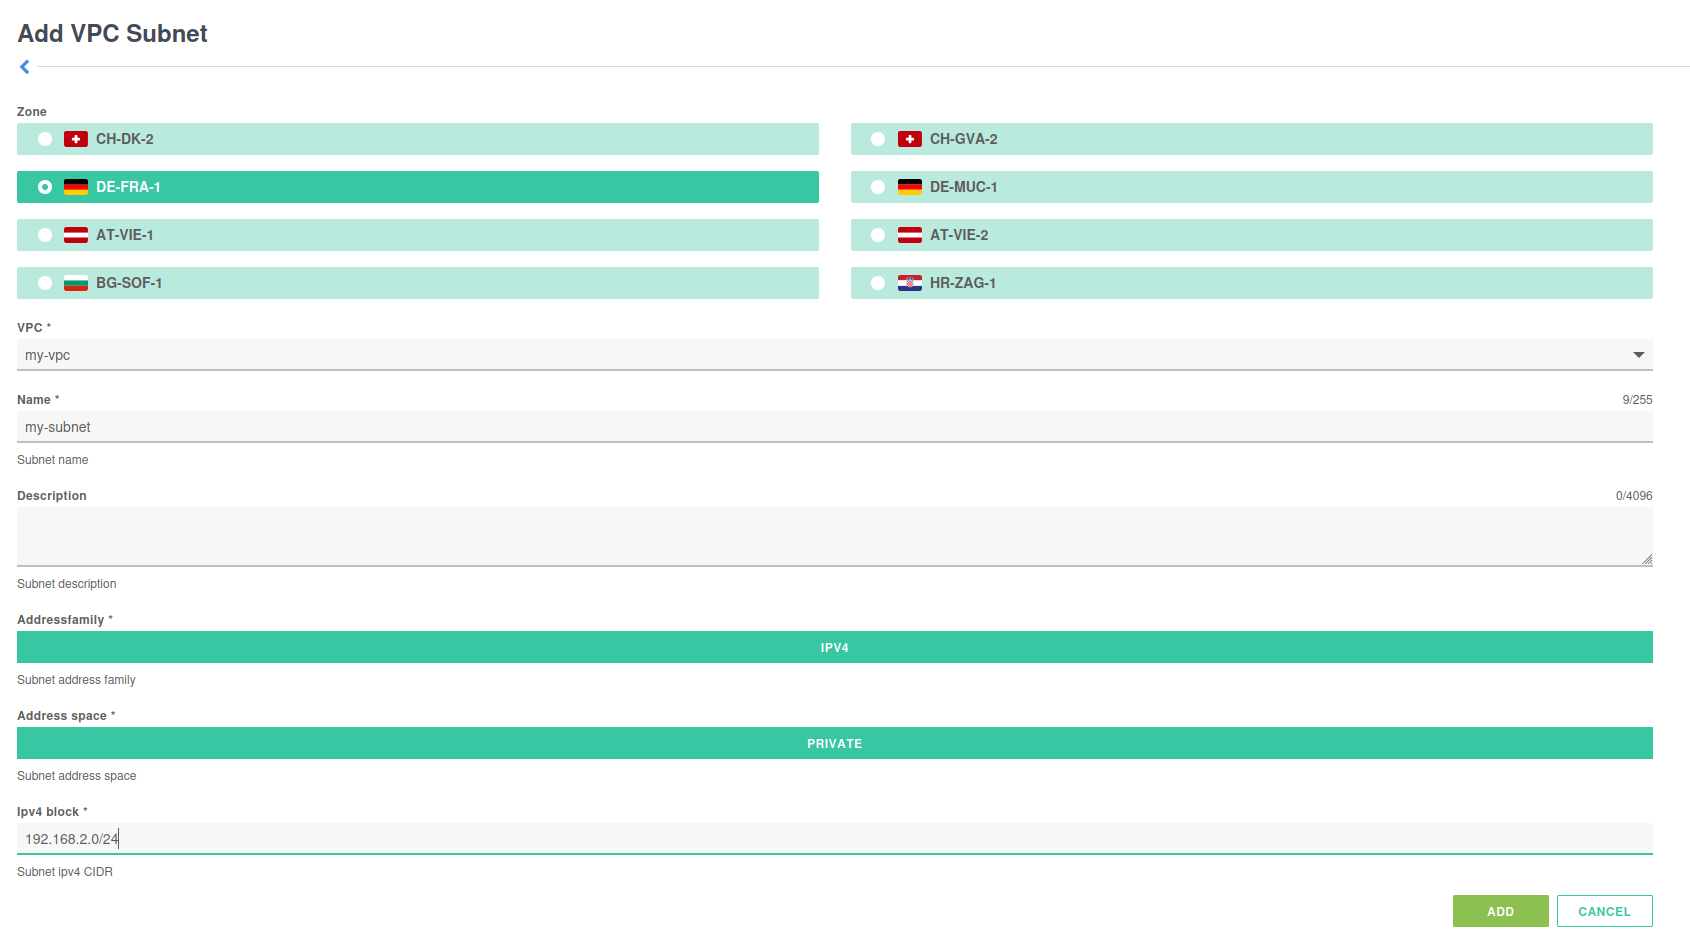
You can then create a Subnet in your VPC. Either by clicking on the VPC and creating a Subnet there, or by going to the Subnet list and clicking the Add button at the top
When creating a Subnet, you need to chose its name and IP range
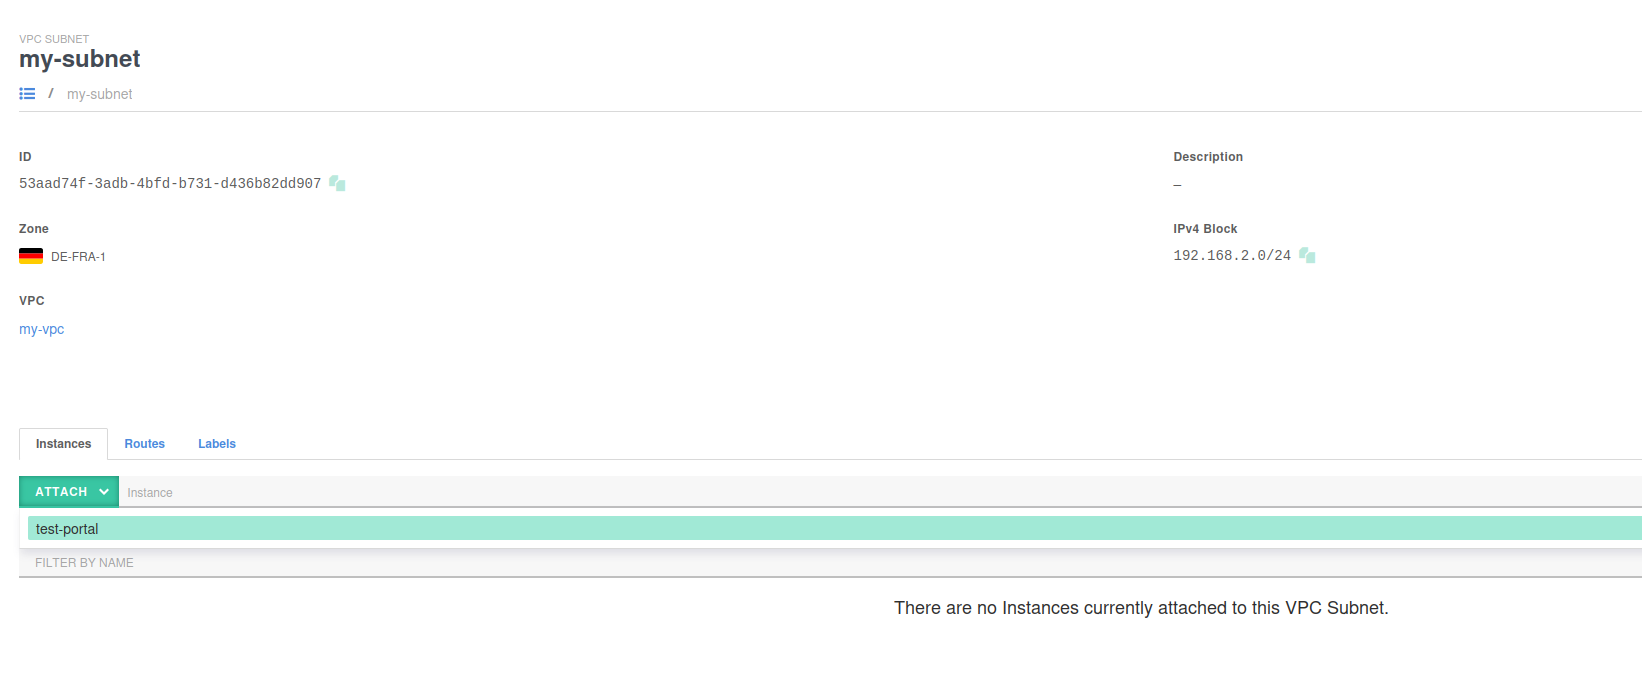
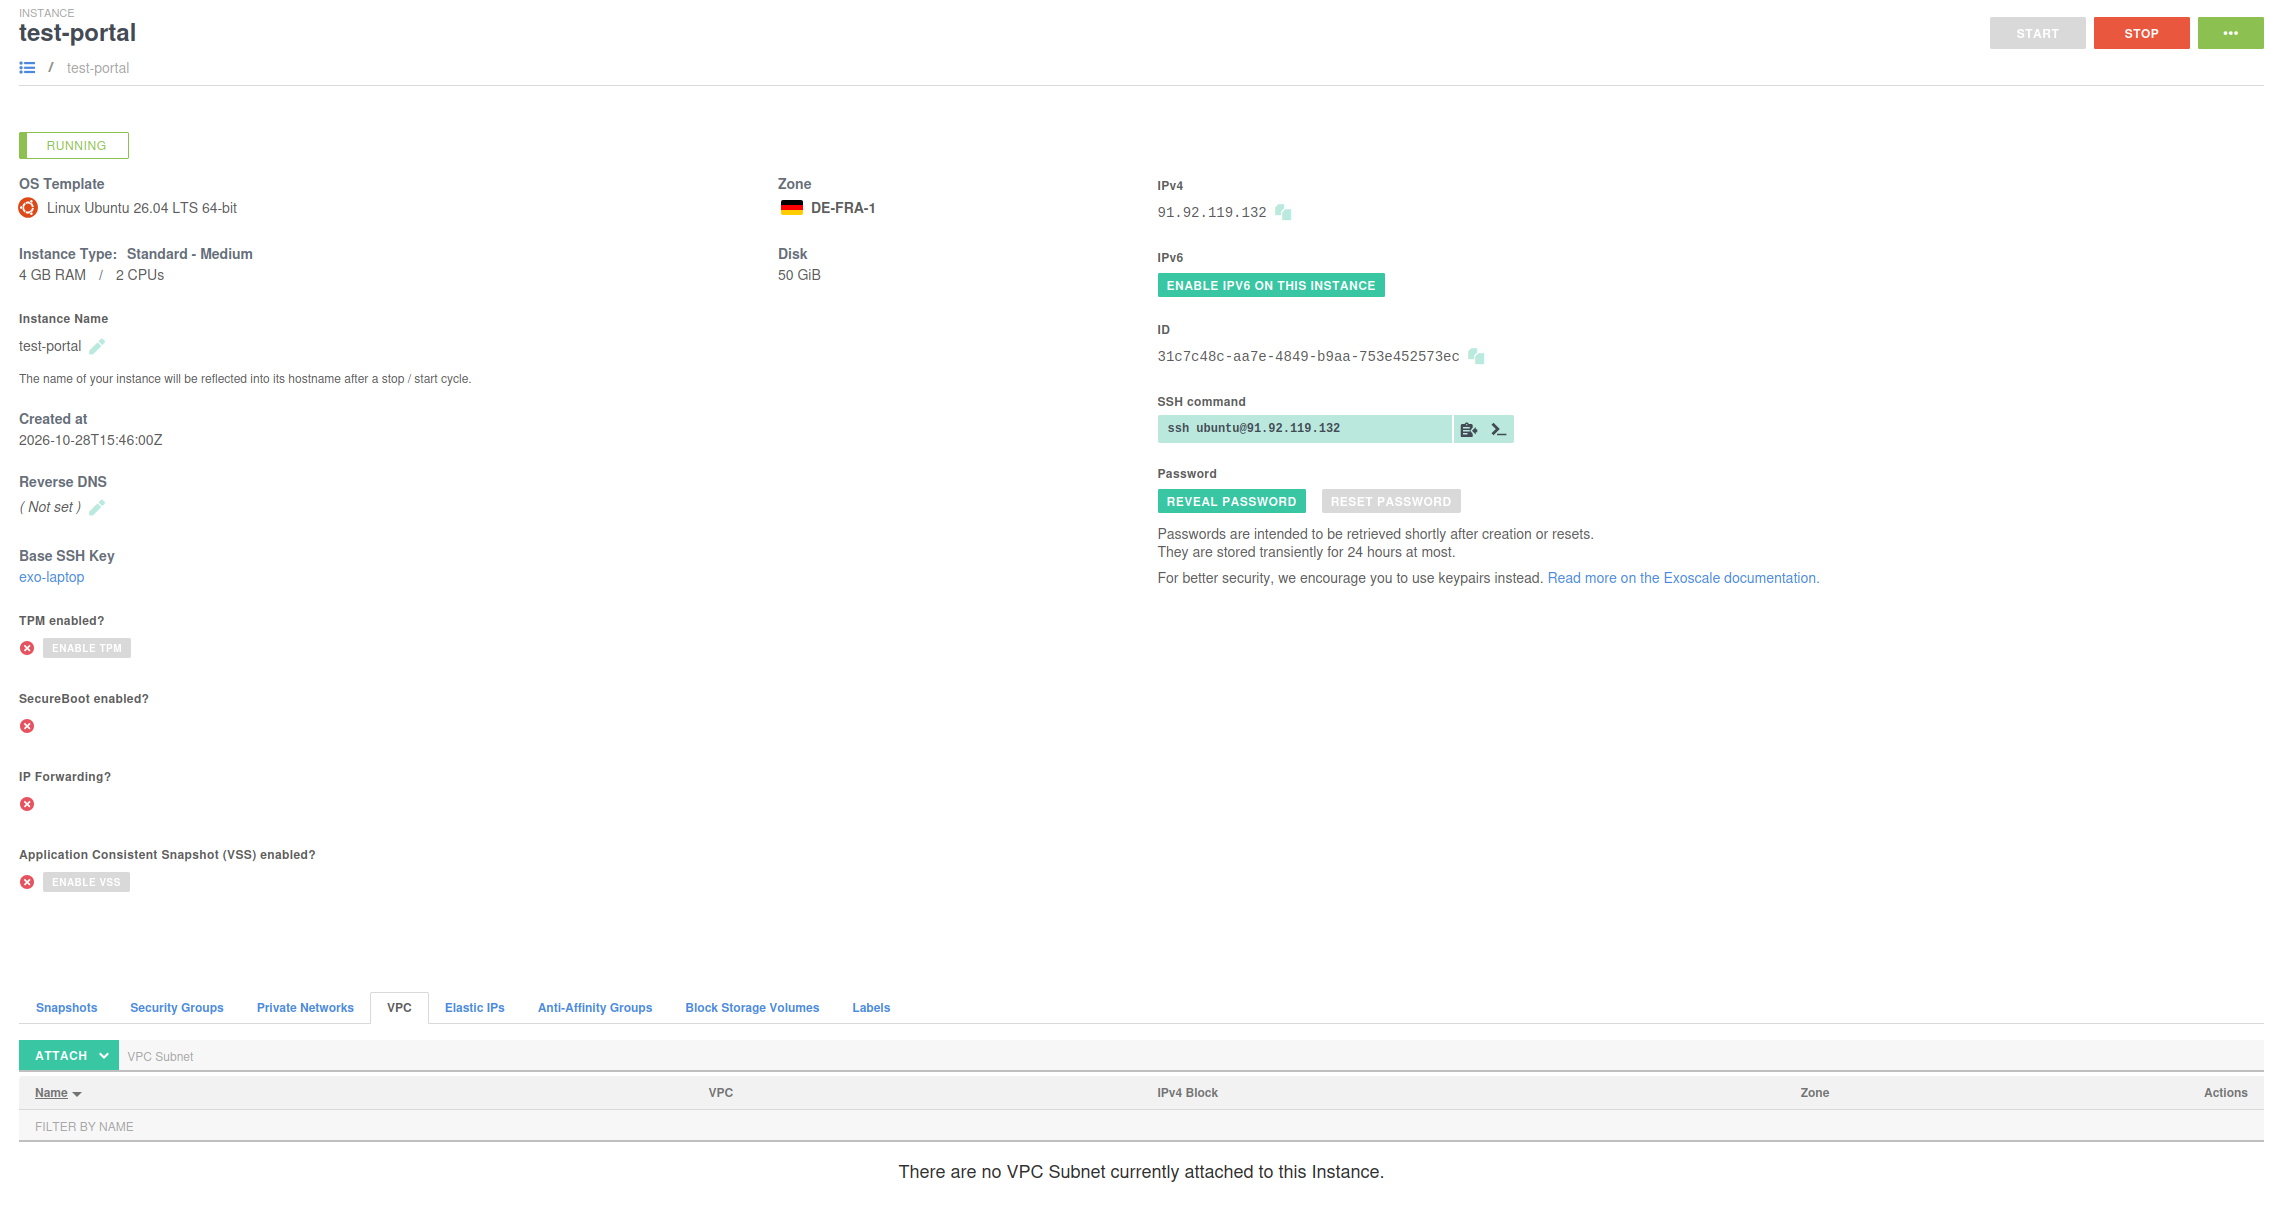
Attach an instance to the Subnet
Once this is done, you can now attach instance to this Subnet. This can either be done from the Subnet view, or directly from the instance view.